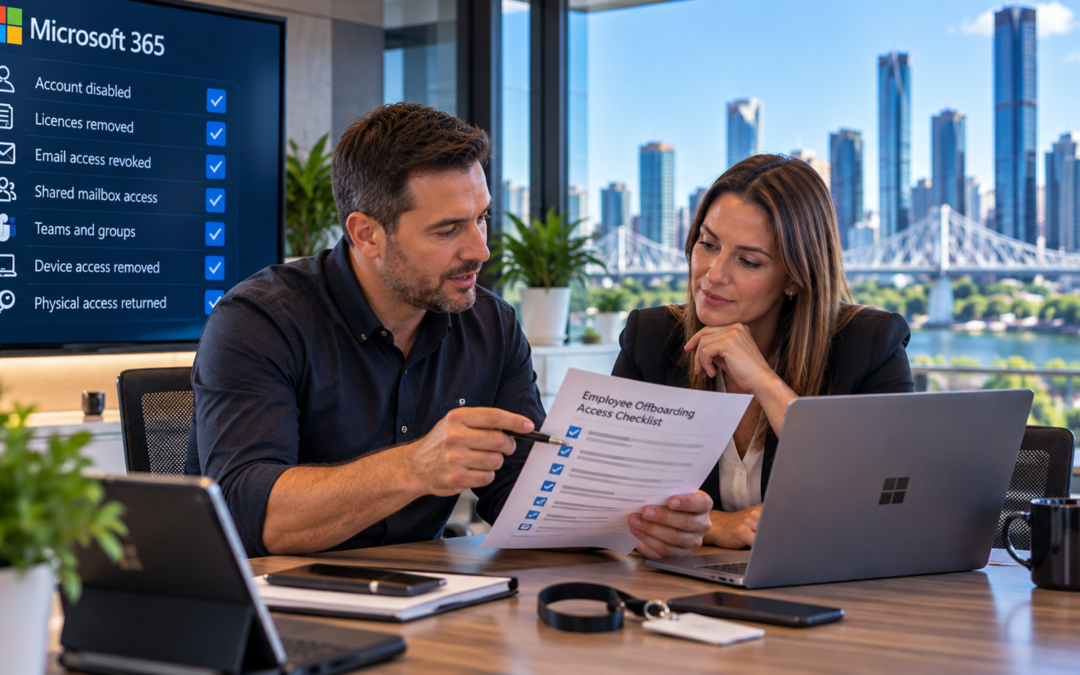
When an employee leaves, collecting their laptop and disabling their email account can feel like the complete offboarding process.
It is not.
A person may have accumulated access to Microsoft 365, business applications, shared passwords, cloud storage, remote-access tools, supplier portals and information stored on personal or company devices.
If that access is not identified and removed systematically, the business can be left with inactive accounts, unmonitored forwarding rules, exposed information and uncertainty about who can still reach important systems.
Effective offboarding protects the departing employee, the remaining team and the organisation.
Key takeaways
- Offboarding should be coordinated between management, human resources and the person responsible for technology.
- The timing of access removal must be authorised and clearly communicated.
- Blocking sign-in does not automatically address every application, device, password or mailbox rule.
- Business information should be preserved before licences or accounts are removed.
- Every completed step should be recorded.
Why disabling email is not enough
A Microsoft 365 account may provide access to Outlook, Teams, OneDrive, SharePoint and other business information.
But most organisations use additional systems, including:
- accounting and payroll platforms;
- customer relationship management systems;
- password managers;
- remote-access or VPN services;
- banking or payment portals;
- cloud applications;
- social media accounts;
- supplier portals;
- project-management systems;
- telephone and messaging platforms;
- building access systems; and
- shared passwords or service accounts.
Access may also continue through active browser sessions, registered mobile devices, application tokens, saved passwords or third-party applications.
The organisation therefore needs an access-removal process - not just an email task.
STEP 01
Confirm authority, timing and responsibility
Technology staff should not guess when to remove access.
Management or the authorised HR representative should confirm:
- the employee’s final working time;
- whether access must be removed immediately;
- whether the departure is routine or sensitive;
- who is authorised to receive the employee’s business information;
- what automatic replies or forwarding arrangements are permitted;
- which devices and physical assets must be returned; and
- who will communicate with the employee.
Sensitive departures may require access to be removed while the final meeting is occurring. Routine departures may allow time for an orderly handover.
Either way, responsibilities and timing should be agreed in advance.
STEP 02
Block Microsoft 365 access and revoke sessions
At the authorised time, the Microsoft 365 offboarding process will usually include:
- resetting the password;
- blocking the user from signing in;
- revoking active sign-in sessions and refresh tokens;
- removing administrative roles;
- reviewing authentication methods;
- reviewing registered devices; and
- checking for unexpected recent sign-in activity.
An employee may already be signed in on a browser, computer or mobile device. That is why changing the password alone should not be treated as the complete access-removal step.
STEP 03
Remove privileged access first
Any account with administrative privileges deserves immediate attention.
- Review roles across:
- Microsoft 365;
- Microsoft Entra;
- device-management systems;
- backup platforms;
- domain and website hosting;
- remote-management tools;
- financial systems;
- security products; and
- important business applications.
Remove unnecessary privileged roles before completing the broader account process.
Where a shared administrative password has been known to the departing employee, change it and update the organisation’s password-management records.
STEP 04
Preserve email and business information
Do not immediately delete the user account.
The mailbox, OneDrive and other business systems may contain:
- client correspondence;
- contractual records;
- project documentation;
- operational procedures;
- work in progress;
- calendar information; and
- evidence required for an investigation or legal matter.
Management should determine which authorised employee requires access to the business information.
Depending on organisational policy, licensing and technical requirements, this may involve:
- converting the mailbox to a shared mailbox;
- granting an authorised person mailbox access;
- configuring a carefully approved automatic reply;
- transferring OneDrive content;
- retaining information under the organisation’s retention requirements; and
- documenting who received access.
Email forwarding should not be applied automatically. It can create privacy, confidentiality and operational concerns and should be explicitly approved.
Legal or regulatory retention questions should be referred to an appropriately qualified adviser.
STEP 05
Review mailbox settings and delegated access
Check more than the mailbox contents.
Review:
- inbox and sweep rules;
- forwarding addresses;
- automatic replies;
- mailbox delegates;
- Send As permissions;
- Send on Behalf permissions;
- mobile-device connections;
- connected applications; and
- unusual recent mailbox activity.
This matters because mailbox changes can persist after an account has been misused.
In one incident handled by OmekaTech, a compromised mailbox had unauthorised rules and out-of-office settings. Messages had been redirected away from the normal inbox, and a malicious PDF had been sent to external contacts.
OmekaTech removed the unauthorised changes, restored affected messages, blocked the identified file through email policy and helped the business notify 18 external recipients.
That was an incident rather than an employee departure, but it demonstrates why account reviews need to include mailbox behaviour - not merely the password.
Client details have been withheld to protect confidentiality. Incident circumstances and outcomes vary.
STEP 06
Remove access to other business applications
Use the employee’s role and access register to identify every relevant platform.
This may include:
- accounting and banking systems;
- CRM and practice-management software;
- password managers;
- cloud file-storage services;
- remote desktop and VPN accounts;
- project and task systems;
- website administration;
- domain and DNS management;
- social media;
- support portals;
- telecommunications portals;
- supplier systems; and
- industry-specific applications.
For each system, disable the individual account or transfer ownership using the vendor’s approved process.
Avoid continuing to use an account created in the former employee’s name simply because other staff know its password.
STEP 07
Recover and secure devices
Create a clear record of every asset issued to the employee, including:
- computers;
- monitors;
- mobile phones;
- tablets;
- security keys;
- access cards;
- storage devices;chargers and docks; and
- specialist equipment.
After recovery, company devices should be checked, backed up where authorised and prepared for reuse using an approved process.
If personal devices were permitted to access business information, review the applicable bring-your-own-device policy and the organisation’s technical ability to remove business access or data.
Do not erase a device before confirming that required business records and potential evidence have been preserved.
STEP 08
Change shared credentials
Shared accounts create accountability and security problems, but many businesses still use them.
Identify any shared credentials the person knew, including:
- Wi-Fi passwords;
- alarm or door codes;
- shared supplier accounts;
- local administrator passwords;
- shared social-media credentials;
- application service accounts; and
- passwords stored outside the approved password manager.
Change affected credentials and distribute the replacements securely.
The longer-term objective should be to replace shared access with individual, auditable accounts wherever the system supports them.
STEP 09
Transfer ownership and operational knowledge
Access removal should not leave an important process without an owner.
Confirm the transfer of:
- recurring tasks;
- client relationships;
- shared mailboxes;
- calendars;
- automation workflows;
- approval processes;
- application ownership;
- supplier contacts;
- subscriptions; and
scheduled reports.
A technically complete offboarding process can still disrupt the business if nobody knows who now owns the work.
STEP 10
Monitor and document completion
Keep an offboarding record showing:
- who authorised the departure;
- the approved access-removal time;
- which accounts were disabled;
- which sessions were
- which devices were returned;
- who received access to business information;
- which shared credentials were changed;
- any exceptions or outstanding actions; and
- who verified completion.
For sensitive departures, consider monitoring for unusual sign-ins, forwarding changes or data activity based on the organisation’s policies and legal obligations.
A practical offboarding timeline
1
Before the departure
- Obtain management or HR authorisation.
- Confirm the final access time.
- Prepare an application and device inventory.
- Identify administrators and shared credentials.
- Confirm the recipient of business information.
- Prepare communications and handover arrangements.
2
At the authorised time
- Reset the account password.
- Block sign-in.
- Revoke active sessions.
- Remove administrative roles.
- Disable remote-access accounts.
- Recover physical devices and access cards.
- Change high-risk shared credentials.
3
After access has been removed
- Review mailbox rules and forwarding.
- Preserve and transfer authorised business information.
- Remove access from remaining applications.
- Update documentation and asset registers.
- Review recent account activity where appropriate.
- Confirm that operational ownership has transferred; and
- Obtain final approval before deleting accounts or licences.
Build offboarding into normal operations
Offboarding should not depend on somebody remembering an informal checklist.
Create a repeatable process involving:
- an authorised request;
- a standard user and device inventory;
- agreed timing;
- assigned technical actions;
- evidence of completion; and
- management confirmation.
Is your access-removal process complete?
OmekaTech helps Brisbane businesses review Microsoft 365 accounts, devices, administrative access, security settings and employee lifecycle procedures.
An Executive Technology and Security Assessment can identify unmanaged accounts, unclear responsibilities and practical opportunities to improve onboarding and offboarding.